


| HEADLINE |
|

Windows 11 zero-day vulnerability raises security concerns
Published : Friday, 20 November, 2026 at 11:35 PM
Observer Online Report


Collected Photo
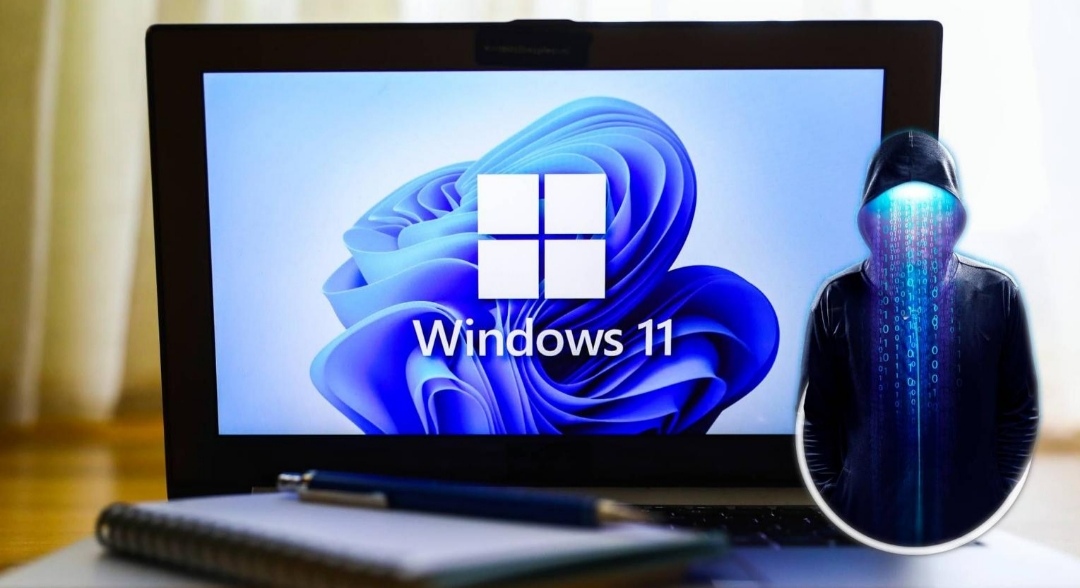
A newly disclosed zero-day vulnerability in Windows 11 has raised security concerns after researchers demonstrated that attackers with physical access to a locked computer could run programmes without signing in.
Dubbed FastUnlock, the flaw exploits Microsoft's built-in Narrator accessibility feature to bypass the lock screen and gain access to a restricted system account. Security firm ThreatLocker independently reproduced the technique, including on a BitLocker-encrypted device running the latest November security updates.
The vulnerability requires physical access and does not grant administrator privileges. Microsoft has yet to release a security patch, while researchers recommend enabling a BitLocker startup PIN to strengthen device protection. No real-world exploitation has been confirmed.
Source: The Hacker News
-AH
Loading...
Loading...
Also read
Editor : Iqbal Sobhan Chowdhury
Published by the Editor on behalf of the Observer Ltd. from Globe Printers, 24/A, New Eskaton Road, Ramna, Dhaka.
Editorial, News and Commercial Offices : Aziz Bhaban (2nd floor), 93, Motijheel C/A, Dhaka-1000.
Phone: PABX- 41053001-06; Advertisement: 41053012; 01793317829, 01550707291, 01550707296
E-mail: [email protected], [email protected]. [email protected], [email protected], [email protected], [email protected], Online-email: [email protected]
Published by the Editor on behalf of the Observer Ltd. from Globe Printers, 24/A, New Eskaton Road, Ramna, Dhaka.
Editorial, News and Commercial Offices : Aziz Bhaban (2nd floor), 93, Motijheel C/A, Dhaka-1000.
Phone: PABX- 41053001-06; Advertisement: 41053012; 01793317829, 01550707291, 01550707296
E-mail: [email protected], [email protected]. [email protected], [email protected], [email protected], [email protected], Online-email: [email protected]


