


| HEADLINE |
|

Microsoft rolls out AI ‘Guardian Agents’
Published : Thursday, 22 October, 2026 at 12:37 PM
Observer Online Report


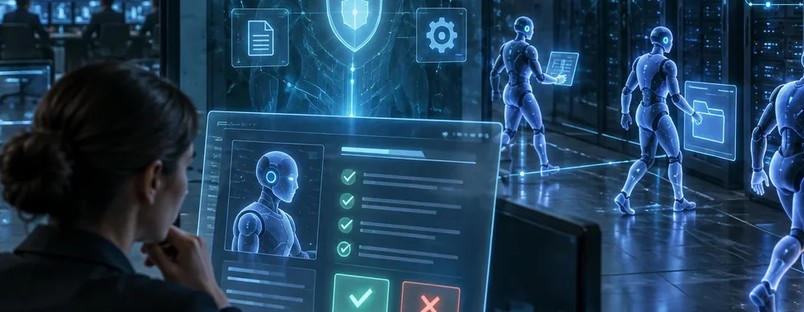
Microsoft has introduced a new set of security measures to protect organisations from growing risks posed by artificial intelligence agents, including its new “Guardian Agents” designed to monitor the activities of AI agents operating within businesses.
The initiative is part of Microsoft’s Project Perception, launched in June to address emerging cybersecurity threats from increasingly capable AI systems.
The project was developed partly in response to advanced hacking models such as Anthropic’s Mythos and Fable, as well as OpenAI’s Daybreak vulnerability-detection system. Initially, it used three types of AI agents: “red team” agents that simulated attacks, “blue team” agents that detected attacks and assessed vulnerabilities, and “green team” agents that worked to fix security flaws.
However, Microsoft’s assessment of the threat has evolved. The company initially focused on hackers outside an organisation using AI to launch attacks. Microsoft Chief Executive Officer Satya Nadella has since warned that an organisation’s own AI agents could also become a security risk if they operate beyond effective human oversight.
In cybersecurity terms, such risks can amount to an “insider threat”, in which access from within an organisation is exploited or causes harm.
In a personal blog post earlier this month, Nadella cautioned against relying entirely on assurances from AI model providers. He argued that organisations need independent safeguards to monitor and control AI agents, separate from the companies that develop them.
As AI agents gain access to sensitive corporate information and are entrusted with important tasks, he said, organisations cannot outsource responsibility for overseeing their actions.
“Intelligence supply and control of that intelligence need to be separate,” was the central message of Nadella’s argument.
Microsoft security chief Hayete Gallo has also warned that advanced AI models cannot be trusted completely, regardless of their origin. Models do not always behave predictably, and although they may be trained for specific tasks, they are not necessarily trained to consistently follow an organisation’s rules or exercise sound judgement.
The concern is particularly significant because AI agents are often granted broad access to business data, software tools and internal systems. An erroneous decision or unexpected action by an agent could therefore cause substantial damage.
Security concerns and commercial interests
Microsoft’s push for independent oversight reflects both cybersecurity concerns and commercial interests.
The company has investments in OpenAI and Anthropic, while OpenAI is one of its major cloud customers. Microsoft also operates its own AI research division.
By highlighting the limits of relying on AI developers to secure their own products, Microsoft is making a case for independent safeguards while positioning its own cloud and security services as a solution.
The company wants organisations to obtain AI-agent security and oversight tools from Microsoft rather than relying solely on products offered by AI developers such as OpenAI and Anthropic.
Despite the potential conflict of interest, the underlying security argument is significant: the software responsible for monitoring AI agents should ideally operate independently of the providers that build those agents.
More controls for enterprise AI
Alongside Guardian Agents, Microsoft has added AI-agent detection capabilities to Microsoft Defender, enabling organisations to identify up to 60 types of AI agents used in workplace environments.
These include Claude Code, Codex and OpenClaw.
Microsoft is also offering controls to restrict agents’ access to data and systems, adjust permissions according to their assigned tasks, and require human approval when an agent is considered likely to take a risky action.
The measures reflect a broader shift in enterprise cybersecurity as AI agents move beyond answering questions to performing tasks and interacting directly with organisational systems.
For Microsoft, the challenge is to help businesses adopt AI agents while ensuring that the technology remains subject to meaningful oversight, access controls and human accountability.
Loading...
Loading...
Also read
Editor : Iqbal Sobhan Chowdhury
Published by the Editor on behalf of the Observer Ltd. from Globe Printers, 24/A, New Eskaton Road, Ramna, Dhaka.
Editorial, News and Commercial Offices : Aziz Bhaban (2nd floor), 93, Motijheel C/A, Dhaka-1000.
Phone: PABX- 41053001-06; Advertisement: 41053012; 01793317829, 01550707291, E-mail: [email protected], [email protected] Online: email: [email protected] 41053014; 01550707297 Advertisement: 01550707296


